Resources
Evaluating a HIPAA Compliant CRM for Patient Acquisition
Deploying a HIPAA compliant CRM for patient acquisition requires far more than signing a vendor Business Associate Agreement. For healthcare networks, outpatient clinics, and specialty practices, the central operational challenge is building an intake workflow that captures patient demand, satisfies federal privacy rules, and preserves conversion attribution back to ad networks. Choosing the right system means evaluating data pipelines from the initial ad click to final admission.
By Mike Hulick, Founder, Marketing Powered
Where Patient Intake Workflows Leak Protected Health Information
What is a HIPAA Compliant CRM in Patient Acquisition?
A customer relationship management platform does not achieve compliance through vendor marketing copy. Under federal law, a platform becomes compliant only when its technical architecture, data handling policies, and physical safeguards satisfy the administrative, physical, and technical standards established under the HHS HIPAA Security Rule. In patient acquisition, the CRM functions as the central intake terminal where public marketing campaigns intersect with protected health operations.
Picture a busy central intake office for a multi-location healthcare network. Three intake coordinators wear headsets, managing incoming calls prompted by local search campaigns. At the same time, online inquiries populate their triage queues from condition-specific landing pages. In a non-compliant workflow, standard commercial software immediately blends the prospective patient's contact information, condition notes, and digital advertising identifiers (such as Google Click IDs or Meta browser IDs) into a single unencrypted customer record. If that software fires browser-level client scripts or passes unredacted form data to third-party marketing tags, protected health information (PHI) is disclosed without authorization.
A compliant acquisition CRM separates clinical intake records from raw advertising identifiers. It allows marketing teams to see which campaigns produce qualified admissions while preventing care coordinators from accidentally transmitting clinical summaries back to digital ad platforms. It replaces client-side webhooks with authenticated, server-side data ingestion, ensuring that prospective patient information is encrypted both in transit and at rest before an intake specialist opens the file.
Modern healthcare marketing systems rarely suffer security breaches through brute-force server attacks. Instead, data disclosures occur during everyday lead generation workflows. Standard web development and digital marketing practices, while standard in retail and software sectors, create severe compliance violations when applied to healthcare organizations.
According to the HHS Office for Civil Rights guidance on online tracking technologies, regulated entities cannot disclose electronic protected health information (ePHI) to third-party tracking vendors without a signed Business Associate Agreement or an explicit HIPAA authorization from the individual. HHS specifically clarified that transmitting an individual's IP address, device identifier, or unique advertising ID alongside metadata that reveals health-seeking intent (such as visiting an oncology, behavioral health, or cardiology consultation page) constitutes an impermissible disclosure.
Data leakage across patient intake pipelines typically stems from three specific components:
- Client-Side Pixel Scrapers: Mainstream advertising scripts running directly inside prospective patients' browsers routinely scan form fields, URL query strings, and button clicks. When a patient completes a consultation request form, native pixels can ingest the form payload or page path before the submission reaches the CRM database.
- Unshielded Call Tracking Integrations: Many voice tracking tools record phone calls, generate automatic transcripts, and assign caller phone numbers to incoming search keywords. When these platforms feed call events into an unconfigured CRM or back to advertising dashboards via standard client tags, medical conditions discussed on the line can be exposed to unauthorized endpoints.
- Third-Party Middleware and Automation Webhooks: Intake teams frequently connect landing page builders to customer databases using consumer-grade automation tools. If these intermediate pipelines lack a valid HHS business associate contract, transmitting names, emails, and health symptoms across those servers breaches federal transmission security standards.
The Federal Trade Commission digital health enforcement actions have confirmed that civil penalties apply when consumer health platforms expose browsing habits and intake responses to commercial ad networks. To understand how these regulatory boundaries apply to your broader acquisition architecture, review our analysis of HIPAA compliant marketing: what the rules mean for campaigns and tracking.
Five Architectural Criteria for Evaluating Healthcare CRM Software
When vetting a healthcare CRM, marketing and IT executives should move past high-level feature summaries. Instead, probe the technical boundaries of each platform using five operational criteria.
1. Enterprise BAA Scope Across All Communications
Do not assume a signed BAA covers every feature within a software suite. Many major CRM providers offer a standard BAA that applies only to core database tables, explicitly excluding integrated telephony, SMS messaging services, or artificial intelligence transcription tools. If your intake team relies on automated two-way SMS to confirm appointments, confirm that the vendor's agreement extends directly to telecommunication pathways and messaging sub-processors.
2. First-Party Ingestion and Identity Decoupling
An enterprise healthcare platform must ingest traffic attribution tokens (such as utm_campaign, gclid, or referrer data) without automatically linking those tokens to personal clinical entries in ways that violate privacy rules. The platform must accept conversion webhooks from private server environments rather than relying exclusively on public client-side JavaScript. This architectural capability ensures that anonymous visitors who browse service lines are never converted into linked health profiles before providing formal consent.
3. Role-Based Access Controls and Field-Level Encryption
Marketing directors require aggregate reporting on lead volume, intake velocity, and cost per qualified admission. They do not need, and should not have, access to an individual patient's medical history, clinical intake assessments, or treatment notes. The platform must offer field-level permissions that compartmentalize sensitive diagnostic details from operational lead status values. Furthermore, verify that data fields containing PHI utilize Advanced Encryption Standard (AES) 256-bit encryption at rest.
4. Server-Side Attribution and Offline Conversion Compatibility
Because healthcare providers operate in sensitive verticals, conventional conversion tracking methods are heavily restricted. For example, Google Ads policy on sensitive categories explicitly prohibits personalized retargeting based on medical conditions or substance abuse history. A capable patient CRM must maintain native API endpoints that export privacy-safe, hashed conversion milestones (such as an intake status change from "Scheduled" to "Admitted") back to enterprise measurement systems without passing along clinical attributes or unhashed personal identifiers.
5. Multi-Location Hierarchy and Audit Logging
Healthcare systems operating regional clinics or multi-site outpatient facilities need hierarchical permission trees. Care coordinators at Location A must not have visibility into intake queues for Location B unless authorized. The platform must also generate immutable, tamper-evident audit logs that record every instance of user access, export request, record modification, and data transfer. These logs are essential for proving compliance during internal compliance reviews and external regulatory audits.
Free Audit
Want a straight read on where your budget is leaking?
Medical CRM Architectures: General Platforms vs. Specialized Patient CRMs
Healthcare organizations typically evaluate three distinct software models for their patient acquisition workflows: customized enterprise commercial CRMs, specialized patient management platforms, and clinical Electronic Health Record (EHR) systems with front-end intake modules.
To visualize how these systems perform in practice, consider an outpatient surgical group evaluating their software alternatives:
Enterprise General CRMs (Configured for Healthcare)
The surgical group's enterprise marketing team prefers tools like Salesforce Health Cloud or an enterprise-tier HubSpot environment covered by an executed BAA. In this setup, system administrators build custom objects to isolate prospective inquiries from validated medical charts.
The primary advantage is marketing flexibility: the group can connect programmatic pipelines, complex lead-scoring rules, and detailed operational dashboards. The trade-off is architectural complexity. The surgical group must dedicate internal engineering resources to write security rules, disable insecure third-party plugins, and build custom server-side data proxies. Without rigorous technical governance, marketing teams can inadvertently turn on default tracking scripts that leak information to external networks.
Specialized Patient CRM and Medical CRM Software
The group might instead select a dedicated patient CRM platform built exclusively for clinical practices. These applications provide turnkey HIPAA compliance out of the box, offering pre-configured intake forms, secure patient messaging portals, and appointment scheduling systems designed around medical workflows.
The challenge lies in campaign optimization. Specialized medical software vendors often operate closed data environments. They rarely prioritize native API integrations with ad platforms, making it difficult for media managers to feed down-funnel admission values back into bidding algorithms. Teams using these systems often find their marketing visibility ends at the initial form fill, leaving media buyers unable to optimize campaigns for actual revenue outcomes.
Clinical EHR Intake Modules
Some health systems attempt to run patient acquisition directly through the patient intake portal of their clinical EHR. While this guarantees regulatory alignment and simplifies medical charting, EHR systems are fundamentally designed for clinical documentation and billing compliance, not commercial patient acquisition.
EHR systems lack agile landing page integrations, cannot ingest granular attribution tags, and offer no mechanism to automate marketing workflows. Relying on an EHR for lead generation forces staff to process incoming inquiries manually, driving up customer acquisition costs and lengthening intake response times. For an in-depth framework on choosing marketing systems partners, see our guide on evaluating HIPAA compliant marketing companies.
Connecting Ad Attribution to Offline Admissions Without Exposing Patient Data
The central operational problem in healthcare growth is closing the loop between advertising spend and final admissions without violating patient privacy. When healthcare systems cannot pass conversion values back to search platforms, bidding algorithms default to optimizing for raw form fills or phone calls. This results in high volumes of unqualified inquiries, administrative waste for intake desks, and elevated patient acquisition costs.
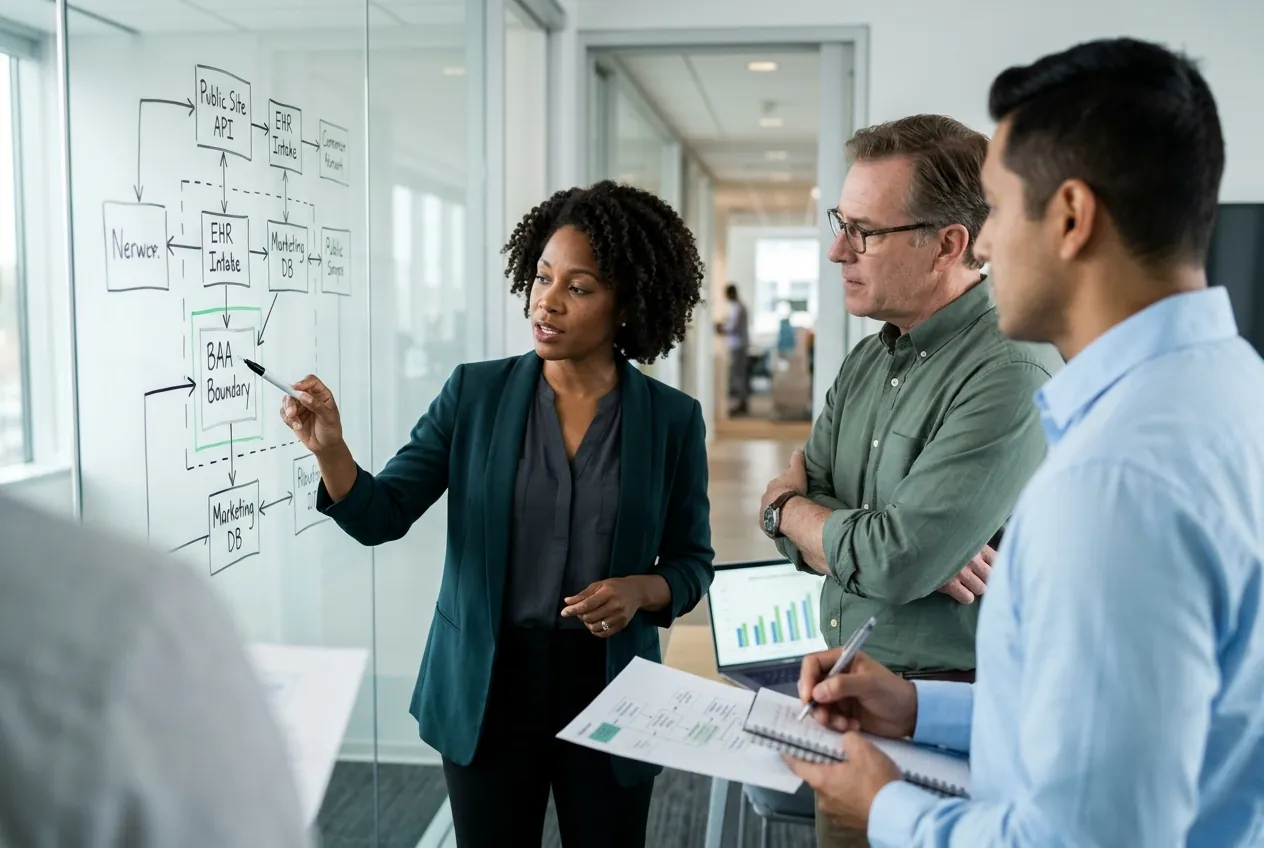
Resolving this issue requires building an offline conversion pipeline that operates entirely on server infrastructure. The diagram below illustrates how attribution data flows independently from clinical intake data:
- Click Capture: A prospective patient clicks an ad for specialized spinal treatment. The landing page receives a click identifier (such as a Google Click ID) in the query parameters.
- First-Party Session Isolation: A secure first-party server infrastructure captures the click identifier and assigns an anonymous, pseudo-random internal transaction identifier. No client-side ad scripts are loaded on the landing page, preventing third-party ad networks from observing the user's interaction.
- Data Segregation at Intake: When the visitor submits a consultation request, the personal details (name, email, phone, medical concern) are encrypted and routed directly to the HIPAA compliant CRM. The click identifier is decoupled from the clinical information and stored in an isolated, encrypted conversion vault linked only by the pseudo-random transaction identifier.
- Care Navigation and Admission: The clinical intake team processes the inquiry inside the CRM, speaks with the patient, reviews medical qualifications, and schedules the procedure. Once the patient attends the appointment and is admitted, the intake record updates to "Admitted."
- Privacy-Safe Offline Postback: The CRM emits an internal webhook containing only the pseudo-random transaction identifier, the milestone timestamp, and the conversion value. The marketing server matches the transaction identifier to the original click identifier stored in the vault, then transmits an encrypted offline conversion event to the Google Ads API.
At no point does the ad platform receive the patient's name, phone number, diagnosis, or clinical notes. Campaign algorithms receive the mathematical signal required to optimize smart bidding strategies toward high-value admissions, while patient privacy remains protected. If you run Google Analytics alongside these workflows, read our detailed technical review on Google Analytics and HIPAA: what healthcare marketers can and cannot do.
Engineering a Privacy-Safe Stack with Marketing Powered
Maintaining both data compliance and commercial growth requires specialized marketing technology engineering. Marketing Powered operates as an operator-led firm that unites media management with healthcare data infrastructure.
Our founder previously served as healthcare Chief Marketing Officer for a treatment network that expanded from 3 to 24 locations, personally managing $1.5 to $2M per month in Google Ads across 11+ behavioral and mental health accounts. Additionally, our founder serves as a court-certified expert witness in advertising strategy. We bring real-world operational perspective to organizations navigating strict regulatory scrutiny.
We structure our engagements around practical technical implementation:
- Decoupled Architecture: We configure data ingestion pipelines that isolate electronic protected health information from conversion tracking parameters, preventing unauthorized tracking disclosures.
- Server-Side Measurement Systems: We design and implement server-side tracking pipelines that run offline conversion loops directly into enterprise ad platforms, maintaining attribution to verified admissions rather than basic form fills.
- Sensitive Vertical Experience: Operating as an AI-native company since 2022, we maintain deep experience with LegitScript-certified advertising verticals and platforms that restrict retargeting based on health conditions.
- Owned Compute Infrastructure: Where clients require local processing for sensitive datasets, we deploy owned, local computing infrastructure for HIPAA-aware inference, keeping proprietary operational data sovereign.
To see how we design and deploy these systems for healthcare organizations, explore our dedicated services for privacy-safe tracking and marketing technology.
Questions, Answered.
A HIPAA compliant CRM is customer relationship management software engineered with the technical, physical, and administrative safeguards required under the HIPAA Security and Privacy Rules. It features data encryption at rest and in transit, role-based access permissions, audit logging, and automated user session timeouts. Furthermore, the vendor must execute an enterprise Business Associate Agreement agreeing to protect all electronic protected health information stored within or routed through the platform.
Yes, but only under specific architectural conditions. Standard platforms can be used if you subscribe to an enterprise-level plan that includes an executed BAA and properly configure the platform to segregate intake data. Using these platforms out of the box with standard client-side tracking scripts, public forms, and unconfigured third-party app integrations creates severe compliance risks. You must deploy server-side proxy environments to shield prospective patient data before it enters commercial databases.
No. A Business Associate Agreement is a necessary legal contract, but it does not dictate how your technical team implements software. If your web developers embed third-party advertising pixels on intake pages, or if your intake team exports unencrypted patient lists to external marketing tools, your organization remains liable for impermissible disclosures. Compliance is determined by your overall systems architecture, not by vendor contracts alone.
Healthcare organizations track campaign performance safely by utilizing offline conversion imports via server-side APIs. Instead of passing personal identifiers or clinical descriptions to Google, your data pipeline captures an anonymous click identifier upon initial engagement and stores it separately from the patient's record. When an admission occurs inside the CRM, a secure server matches the transaction event to the original click identifier and sends an encrypted postback to the ad platform, protecting patient identity while training bidding algorithms.
Electronic Health Record platforms are designed specifically for clinical documentation, patient charting, prescription management, and medical billing. They lack the digital marketing infrastructure required for modern patient acquisition, such as dynamic landing page integration, multi-channel intake routing, automated lead nurturing, and offline attribution APIs. Attempting to use an EHR as a marketing CRM slows down intake response times and prevents marketing teams from measuring acquisition efficiency. Request a privacy and tracking review of your marketing stack
Ready to see where your marketing can improve?
Request a free audit of your paid media, landing pages, attribution, and measurement setup. You'll get a straight assessment of where the opportunities are.
or email us at info@marketingpowered.ai